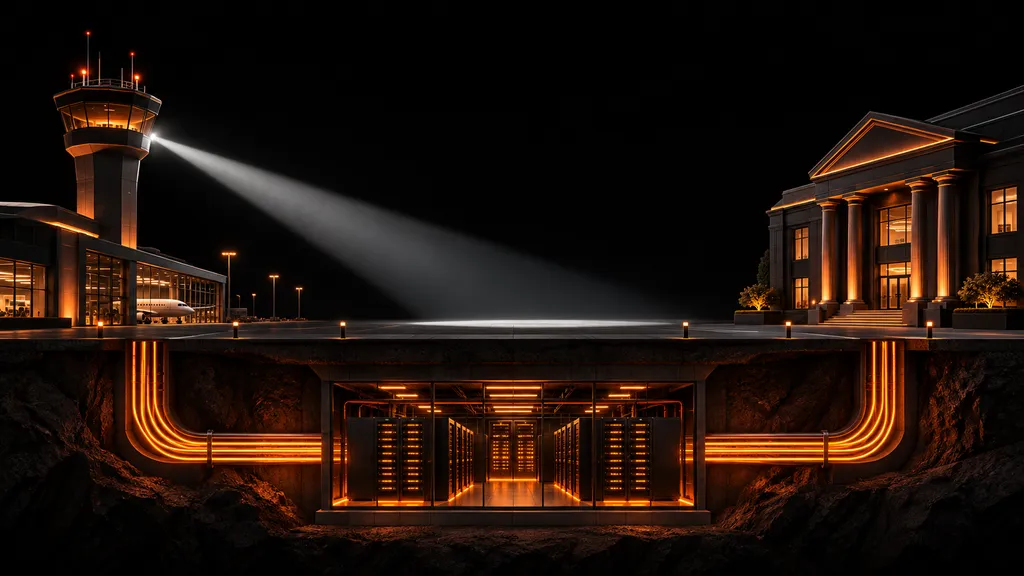
On November 13, the FAA halted departures nationwide after a surge of connection attempts overwhelmed legacy network equipment. Six days later, JPMorgan Chase disclosed that attackers had targeted vendors holding customer marketing data, including names and email addresses. The FAA reported no indication of a cyberattack. Chase confirmed one, and said it was separate from the software bug that disrupted its banking services earlier that week. Federal Aviation Administration
Those details matter when you decide what to fix. Aging equipment can fail under legitimate traffic. Customer data already in a vendor’s possession needs protection wherever that vendor stores it. And then there’s a risk much closer to home, one you can test against your own infrastructure today. Which of your private services will answer a complete stranger on the internet?
A login screen is already an answer
Picture a bank’s reconciliation tool. Twelve employees use it to match the day’s transactions. Because those employees work across three offices, someone gives the tool a public address and puts it behind a login screen.
Now anyone can reach that screen. A stranger still needs credentials to view a transaction, but the application is already accepting connections and processing requests from people who have no business using it. All that exposure exists to serve twelve people.
That’s the problem we built Project Zero to solve. Built on OpenZiti, Project Zero lets a team share a service over a private network, give it a private address, and control which identities can connect. Once the public route is closed, those twelve employees can still open the tool from their enrolled devices. An outsider scanning the bank’s public addresses gets no response from the reconciliation service. Even knowing its name doesn’t give them a route to it. Project Zero
Give the vendor one connection
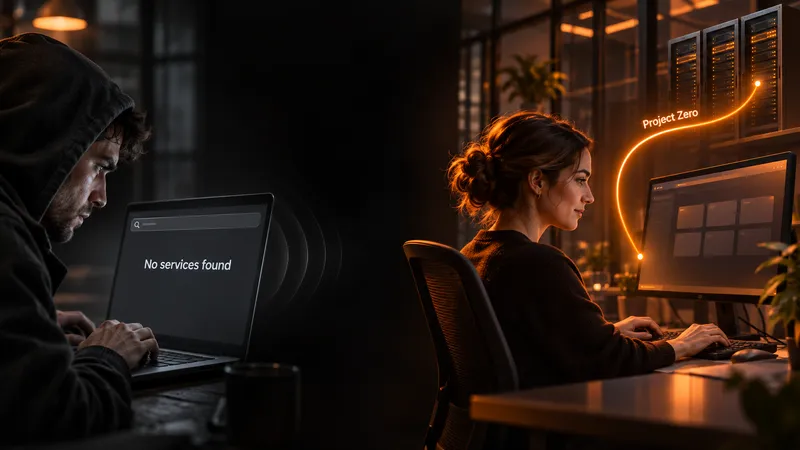
Consider an airport that hires a contractor to maintain its baggage monitoring system. The technician needs to read equipment status and diagnose a stalled conveyor. That job calls for a connection to one maintenance application. It gives the technician no reason to reach the badge-management console or the finance database.
With Project Zero, the airport can share the maintenance application with the contractor’s enrolled device and keep those other services outside its access policy. If that device is compromised, the maintenance application still needs its own safeguards. But the attacker doesn’t inherit a route to every other system simply because the contractor had a reason to connect to one. Project Zero
Pick one service your team uses every day. Maybe it’s the SQL database behind your reporting dashboard, or the remote desktop connection your bookkeeper uses on Fridays. Ask who actually needs it. Then ask why anyone else can reach it.
When the answer is “because we’ve always had that port open,” you’ve found a good place to start. Explore Actieve Project Zero
Need enterprise-grade OpenZiti management? Use NetFoundry.
Giving one airport technician access to one maintenance application is straightforward. Now imagine managing that access across forty airports, each with its own contractors and maintenance schedules. When a contract ends, who removes access? When an auditor asks who changed a policy, where does your team find the record?
Project Zero makes it easy to share individual services privately. For organizations managing OpenZiti across an enterprise, NetFoundry offers a fully managed platform with audit logs for administrative changes. Teams that need to operate the network in their own environment can use NetFoundry’s self-hosted management suite. Project Zero
Actieve is an authorized implementation partner for OpenZiti and NetFoundry. We can help you map which employees, vendors, and applications need to reach each service, then design, deploy, and operate the network around those requirements. Compare Project Zero and NetFoundry.